Attacks don’t keep
office hours.Neither does your exposure.We watch, detect and
respond — 24/7.
Most serious attacks unfold overnight, at weekends, or across systems that nobody’s watching together. Softenger runs detection and response as one operation: a 24/7 Security Operations Center fed by managed endpoint security and network defence — so an attack that starts on a laptop and moves across your network is seen as one story, and stopped.
Endpoint, network and SOC watching in isolation miss the story.
Round-the-clock SOC
Endpoint + network + SOC
Your stack or ours
Not tools without people.
Alerts nobody reads don’t stop anything.
Not separate silos.
Endpoint, network and SOC watching in isolation miss the story.
Not business-hours coverage.
Attacks don’t wait for Monday.
Why attacks go unnoticed
Nobody’s watching at 3 a.m.
Lean teams can’t staff round-the-clock monitoring — and attackers know it.
Alerts outnumber people.
Security tools generate more alerts than any team can triage, and the real one hides in the noise.
Signals live in silos.
Endpoint, network and cloud tools each see part of an attack; nobody connects them.
Detection without response is too slow.
Spotting a threat isn’t stopping it. Containment needs people with the authority and the playbook to act.
Three layers, one operation
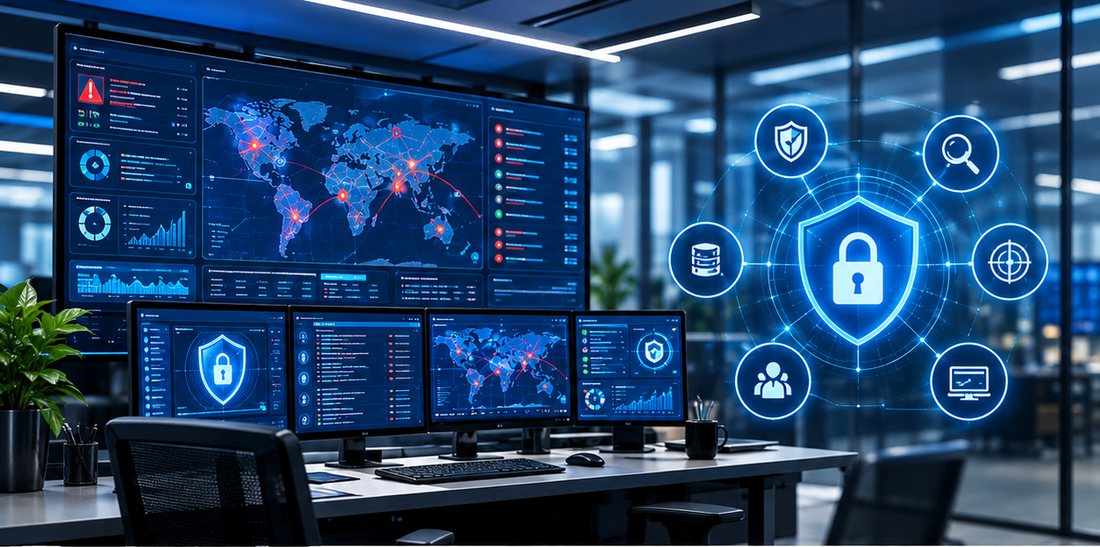
Round-the-clock monitoring, triage, threat hunting and incident response — with industry and regional specialisations.
Managed EDR/MDR, endpoint protection, hardening, and server & workload protection — feeding the SOC.
Managed firewalls, IDS/IPS, network detection & response, segmentation, secure web gateway and zero trust access — feeding the SOC.