Your applications, APIs and cloud are where your business meets the internet.
Find what’s exposed.
Fix what matters.
Prove it’s closed.
Every release, every new API and every cloud change shifts your attack surface. Softenger helps the teams who build and run it stay ahead: testing what an attacker could exploit, keeping vulnerabilities down continuously, building security into how software is made, and securing the cloud it runs on.
Every release, every new API and every cloud change shifts your attack surface.
Prove what’s exploitable
SLA-driven, verified
Code, pipeline, cloud
Not a scanner report and goodbye.
Findings without fixes don’t reduce risk.
Not security that slows releases.
It has to fit how you ship.
Not testing once a year.
Your attack surface changes every week.
Four reasons exposure outruns the team
Every release changes the attack surface.
New features, APIs and cloud resources ship faster than anyone reviews them.
Scanners produce lists, not answers.
Thousands of findings, little sense of which are genuinely exploitable.
Fixing is where it stalls.
Findings pile up because patching, ownership and verification are nobody’s job.
The cloud is configured by many hands.
Misconfigurations and over-permissioned identities appear daily.
Four ways we help you test and defend
Vulnerability Assessment & Penetration Testing (VAPT)
Prove what an attacker could do.
Human-led testing of web applications, networks, APIs and mobile apps.
Best forBefore a launch, after major changes, or for an audit or customer requirement.
Explore →Enterprise Vulnerability Management (VAVM)
Keep exposure down, continuously.
Scanning, risk-based prioritisation, patching and remediation — verified closed, against SLAs.
Best forOrganisations with a growing backlog and no time to work through it.
Explore →Application & API Security
Build security into how software is made.
Security testing, secure code review, DevSecOps, API security and WAF management.
Best forEngineering teams that ship often and want fewer flaws reaching production.
Explore →Cloud Security
Secure the cloud you run on.
Posture management, assessments, Kubernetes security, identity governance and multi-cloud security.
Best forOrganisations on AWS, Azure or GCP that need configuration and access under control.
Explore →Build. Test. Fix. Secure the platform.
Each one reduces the work of the next — fewer flaws shipped means fewer found, and fewer found means faster fixing.
Start with the question you’re asking
-
 01
“Could an attacker actually break in?”
VAPT
-
 02
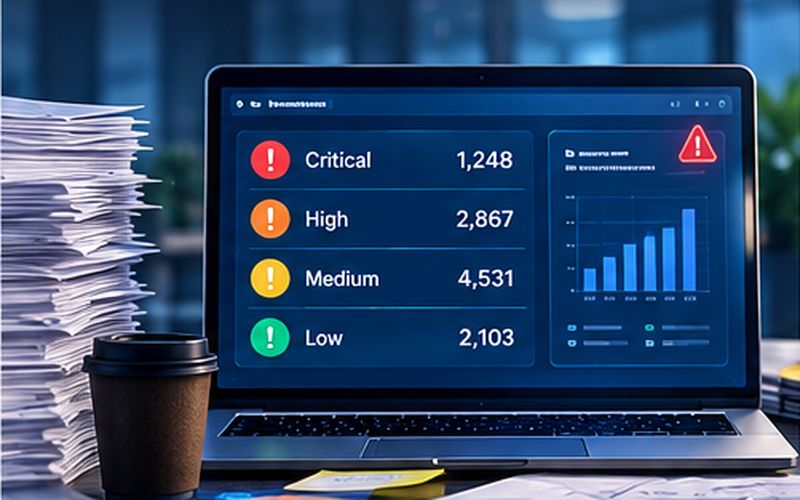
“We have thousands of findings and can’t keep up.”
Vulnerability Management
-
 03
“Our developers ship flaws we only find later.”
Application & API Security
-
 04
“We’re not sure our cloud is configured securely.”
Cloud Security Assessment
-
 05
“A customer wants a pentest report.”
Web Application Penetration Testing
Every engagement follows a framework — not a formula.
Four phases, in a fixed order: map where exposure comes from, spend effort where the risk is, fix it in the pipeline, then keep pace with every release.
Phase 01Advise
Map your applications, APIs, cloud and current testing — and where exposure comes from.
A clear view of your attack surface.
Phase 04Support
Keep testing, fixing and governing as you ship.
Security that keeps pace with your releases.
Phase 02Optimize
Prioritise by real risk, and choose the right mix of testing, fixing and building in.
Effort where it matters.
Phase 03Transform
Test, remediate, embed security in the pipeline, and harden the cloud.
Exposure measurably reduced.
Why teams that ship choose Softenger
Certified where it’s audited. Aligned where you’re regulated.
ISO 27001:2022 and ISO 9001:2015 certified. Delivery aligned to DPDP, PCI-DSS, SOC 1 & SOC 2, HIPAA and CERT-In, run from India.
Talk to our team → ISO 27001:2022
 ISO 9001:2015
 DPDP
 PCI-DSS
 SOC 1 & SOC 2
 HIPAA-Aligned
 CERT-In Aligned
 India-Based Delivery
Questions we get before the first call
VAPT is point-in-time, human-led testing that proves what an attacker could exploit. Vulnerability Management is the continuous programme that scans, prioritises, fixes and verifies. They work best together.
Penetration testing finds flaws in finished applications. Application & API Security builds security into how software is made, so fewer flaws reach production in the first place.
It secures the cloud environment your applications run on — configuration, posture and identity — so the platform underneath is as secure as the code on top.
No. Softenger isn’t currently on CERT-In’s published list. Where empanelment is required, we’ll say so upfront and can coordinate with an empanelled auditor.
If you need proof of what’s exploitable, start with VAPT. If you’re drowning in findings, start with Vulnerability Management. If you’re unsure about your cloud, start with a Cloud Security Assessment.
Stay ahead of every release.
Scope a penetration test — or tell us where you’re stuck. We’ll show you what’s exposed across your applications, APIs and cloud, and the fastest way to close it.